01
Identify Exposure Across Critical Systems
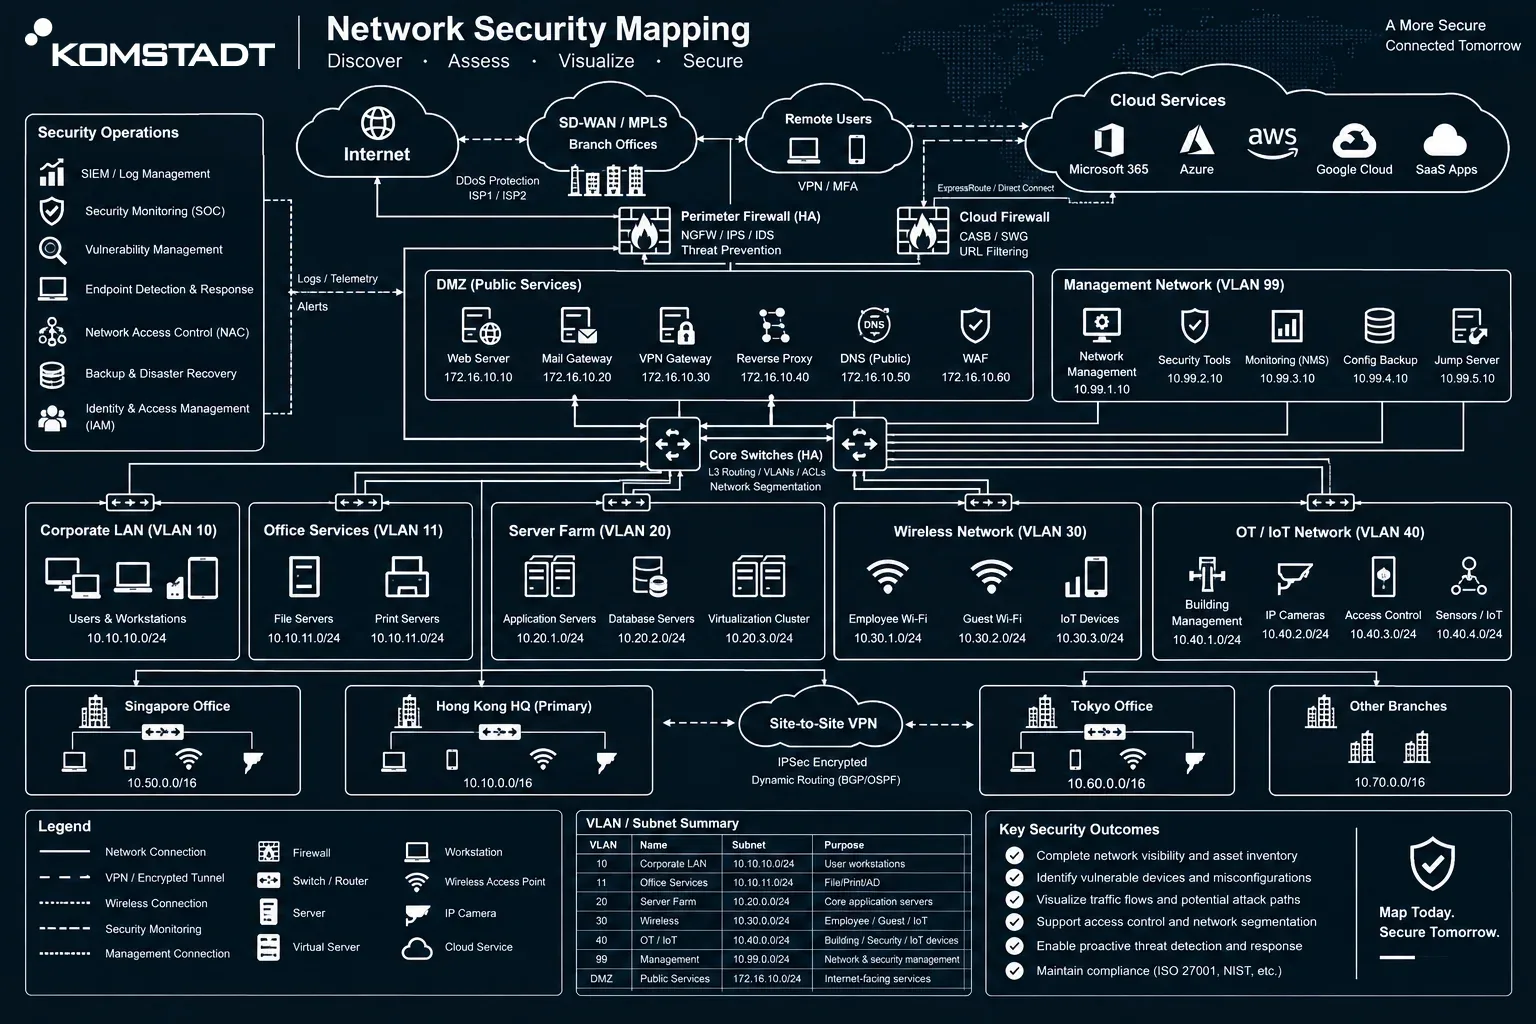
Review the network, servers, endpoints, cloud services, trading platforms and connected infrastructure so management can see what is actually in the environment and where potential weaknesses may sit.
Managed Services
A structured service that helps organisations understand vulnerabilities, test defences, document risks and build practical remediation plans—especially for firms that need stronger assurance in regulated environments such as financial services.
Why This Service Matters
For financial institutions, trading firms and other regulated businesses, uncertainty around system exposure can become a serious governance issue. This service helps identify where vulnerabilities may exist, how those risks affect the operating environment and what remediation path is needed to reduce exposure with confidence.
Review the network, servers, endpoints, cloud services, trading platforms and connected infrastructure so management can see what is actually in the environment and where potential weaknesses may sit.
Highlight vulnerabilities, weak controls, unsupported software, poor patching, outdated operating systems and end-of-life equipment that may increase cyber, compliance or operational risk.
Translate findings into practical actions, SOP improvements and a structured remediation plan that supports stronger governance and better readiness for licence-renewal discussions.
Service Scope
The engagement scope can be adjusted depending on whether the client needs a baseline review, deeper testing, remediation planning or a more complete audit-readiness exercise.
Discover the current network structure and record available assets including servers, switches, firewalls, endpoints, wireless infrastructure, cloud services and business-critical platforms.
Test likely exposure points to identify vulnerabilities that may be exploitable by external threats, internal misuse or weak configuration.
Produce a security report summarising findings, risk observations and priorities, then help prepare or update SOPs and remediation procedures to address those gaps.
Common Risk Focus Areas
These are the types of exposure points that frequently need attention when firms want to strengthen controls and prepare a more disciplined remediation plan.
Risk Focus 01
Identify misconfigurations, missing updates and weak control settings across systems, network devices and endpoints.
Risk Focus 02
Spot obsolete platforms, unsupported versions and applications approaching or past end of support.
Risk Focus 03
Assess whether business-critical and trading-related applications introduce additional operational or cyber exposure.
Risk Focus 04
Separate urgent actions from medium-term improvements so management can plan remediation properly and in sequence.
Financial Sector Relevance
Rather than listing every SFC licence type, this service is positioned to show regulated firms that Komstadt understands the needs of selected trading and financial-market environments and can help turn technical findings into a practical risk-reduction plan.
Operational environments where user access, connectivity, platform resilience and endpoint security all matter.
Trading-related technology environments that need clearer visibility of vulnerabilities and infrastructure health.
Firms that need better governance over systems, data access and supporting technology controls.
Organisations that rely on critical platforms, connected systems and structured operational discipline.
Review the environment and document where weaknesses may exist across infrastructure, platforms, software, operating systems and business-critical services.
Prioritise findings, build a remediation plan, improve SOPs and address the issues that most materially affect security, resilience and governance.
Give management a more structured path toward demonstrating that vulnerabilities have been identified, reviewed and actively addressed.
Planning guide
Security assessments are most useful when the findings identify affected systems, business impact and specific next steps rather than an undifferentiated vulnerability list.
Depending on the agreed scope, an assessment can review networks, endpoints, servers, cloud services, outdated software, access controls and supporting documentation.
A prioritised remediation plan translates findings into responsibilities and next steps, helping teams decide which operational and security improvements to address first.
Assess each finding in context of its likelihood, potential impact, existing safeguards and remediation effort. The resulting priorities can guide owners, sequencing and follow-up checks.